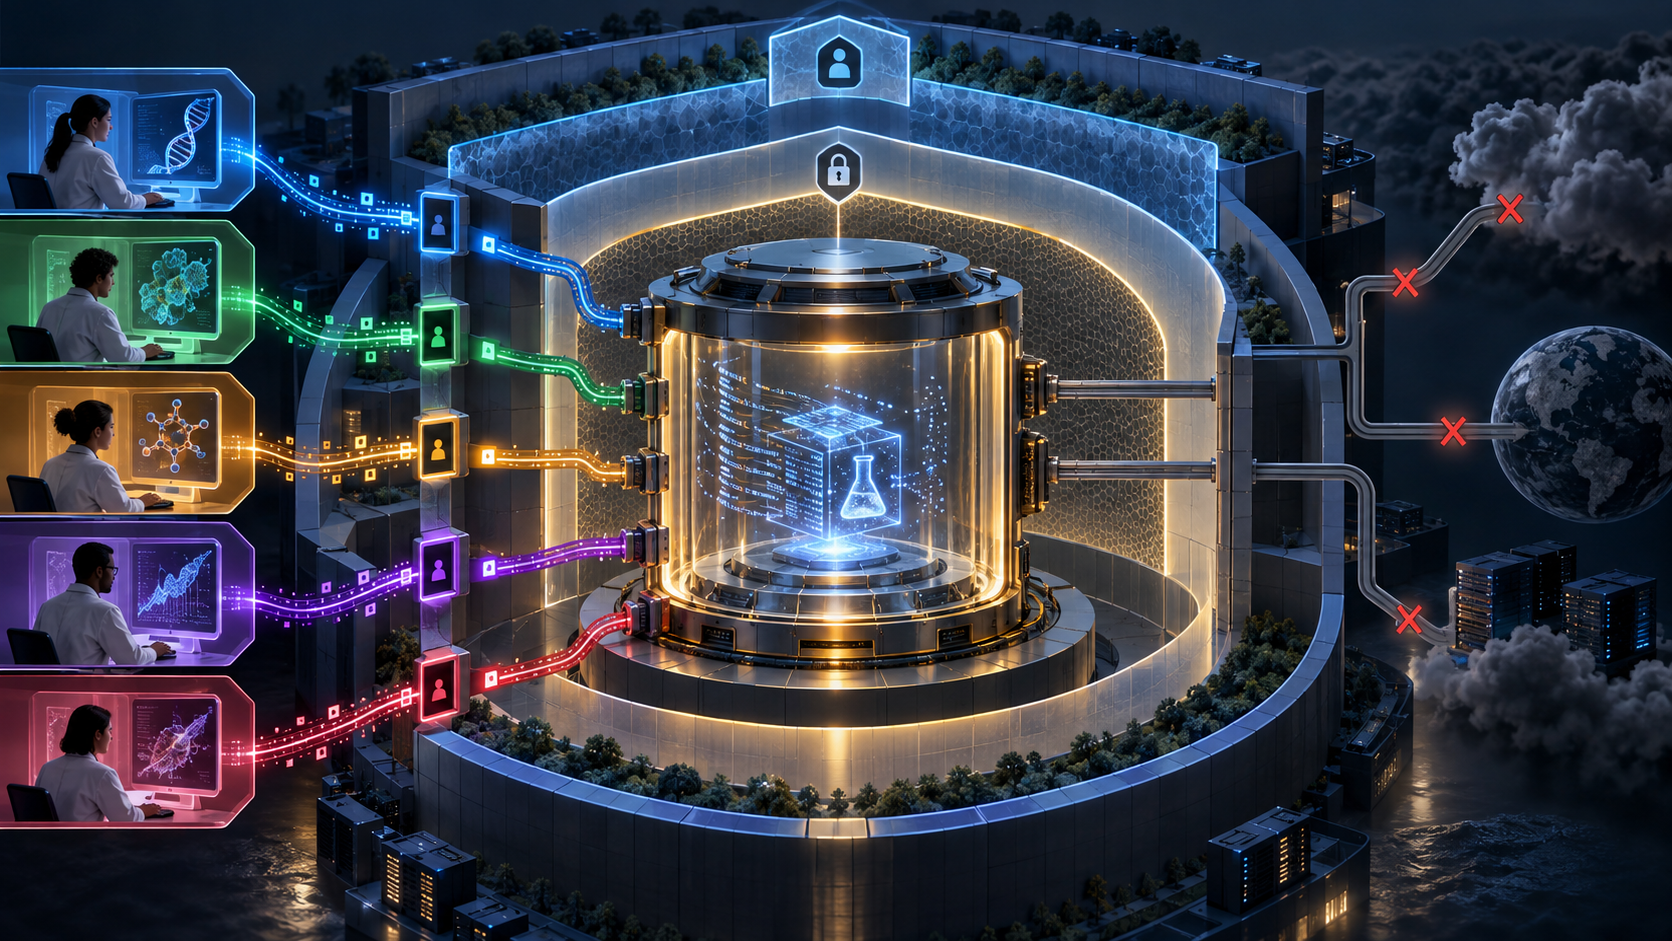
Benchling’s primary-source case study describes a security design for executing agent-generated scientific code across thousands of tenants. The reported architecture addresses two simultaneous requirements: each execution session must remain isolated, while access control must avoid a separate identity role for every tenant. The result is a layered pattern rather than a claim that one control solves the entire problem.
What the evidence says
In its account, AWS Machine Learning says Benchling runs Amazon Bedrock AgentCore Code Interpreter in Amazon Virtual Private Cloud mode. The source describes AgentCore as a platform for building, connecting, and optimizing agents across different frameworks and models.
Benchling’s application reportedly generates scientific code for researchers distributed across thousands of tenants. The stated security requirement is full isolation for every execution session. At the same time, the design cannot depend on one AWS Identity and Access Management role per tenant because the account characterizes that approach as unsustainable role sprawl at this scale.
The reported alternative combines account-level isolation, Route 53 Resolver DNS Firewall, and VPC endpoint policies. The source says these controls help restrict data exfiltration and enforce data access at the individual-job level. These statements come from a single primary account and should be understood as reported design claims, not independently established results.
Operator implications
Operator analysis: the useful pattern is the separation of security responsibilities. Session isolation addresses boundaries between executions. Job-level authorization narrows what each run may access. DNS filtering and endpoint policies constrain possible outbound paths. Account-level isolation adds another boundary around the execution environment.
This decomposition gives operators a clearer review model. Instead of treating tenant identity, code execution, data access, and network egress as one broad control problem, each can be evaluated as a distinct enforcement point. The reported avoidance of per-tenant roles also highlights a practical constraint: an isolation model must remain manageable at the tenant scale it is meant to protect.
The concrete move is therefore architectural: run the interpreter within a controlled network environment, isolate execution sessions, attach access decisions to jobs, and apply network controls intended to limit exfiltration paths. The evidence supports this as Benchling’s reported approach, but it does not establish that the same configuration is sufficient for every workload.
Limits and open questions
The single primary account is not independently confirmed. The evidence pack does not establish whether the controls received third-party testing, how isolation was validated, whether security incidents occurred, or what residual risks remain. It also provides no measurements for cost, latency, operational overhead, or behavior across different framework and model combinations.
The account says the controls help prevent exfiltration; it does not demonstrate absolute prevention. Operators would still need evidence appropriate to their own workloads, tenant boundaries, data-access rules, and threat assumptions before judging whether the pattern is sufficient.